Notice that X25519 and Ed25519 use different encodings for the EC factors, so they are not directly suitable and require conversion if you want to use the same public-private key pairs. The Superior Encryption Normal (AES) is a specification for the encryption of digital data established by the us In addition to AES, Suite B consists of cryptographic algorithms for hashing, digital signatures, and key exchanges.
What’s Elliptic Curve Cryptography?
This step is required in our instance https://alstatenews.com/top-5-reasons-to-order-2d-animation-from-an-outsourcing-studio.html to provide Suite B cipher suites desire. If you do not want to provide Suite B cipher suites preference, you don’t have to carry out this step. The Python binding to the Networking and Cryptography (NaCl) library (PyNaCl) implements many modern cryptographic algorithms, together with the EC level arithmetic over the Curve25519 and Ed25519 signatures.
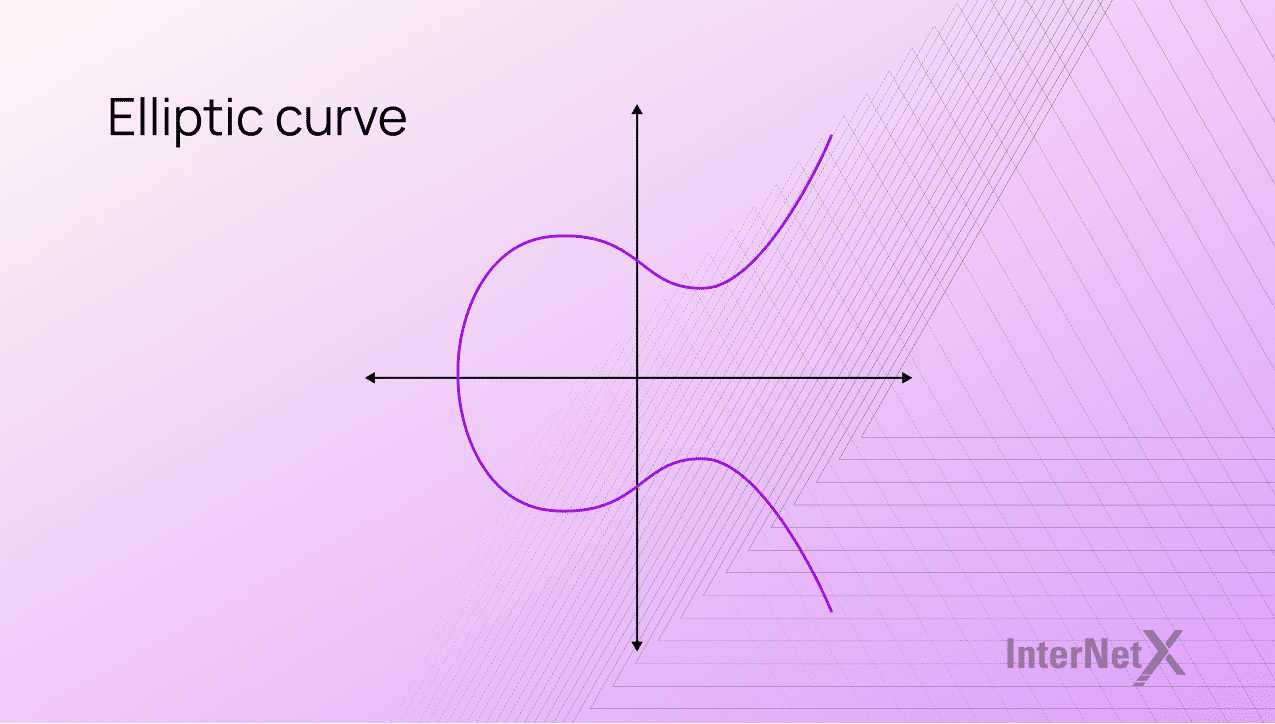
- If we wish a pc to perform level addition, we have to turn the geometric technique into an algebraic method.
- Decide two totally different random factors with totally different x worth on the curve, connect these two factors with a straight line, let’s say \(A\) and \(B\).
- Elliptic curve cryptography is not solely mathematically sound—it is more and more embedded in digital infrastructure.
- We use 192-bit curve within the above example just to make the sample output smaller.
Strengths Of Ecc
One of ECC’s greatest advantages is its capacity to achieve cryptographic strength efficiently. While RSA requires very giant keys to provide a excessive degree of safety, ECC presents comparable protection with a fraction of the necessary thing measurement. That asymmetry is precisely what public-key cryptography needs, and it ensures that a non-public key cannot be easily inferred from the basic public info. While it’s simple to move ahead and compute this point—even after tens of millions of steps—working backward to discover the unique quantity is computationally infeasible. To perceive how elliptic curve cryptography works, it helps to interrupt it down into a number of foundational ideas with out going too deep into advanced mathematics. ECC keys have a shorter key size and require much less power, which is important to be used in embedded systems, such as cellular or IoT devices, and for sooner load instances.
It turns out that the answer to this drawback also permits digital signatures. The one way perform “signs” a doc in order that no person else can forge the signature or the document. The a method operate I Am going to explain in this weblog uses elliptic curve math over finite fields. This method has shorter keys and extra safety than different methods, but it is a bit out of the way in which for many engineers. ECC crypto algorithms can use totally different underlying elliptic curves. Completely Different curves present different degree of security (cryptographic strength), completely different efficiency (speed) and different key length, and also might involve completely different algorithms.
Let’s Meet At A Secret Coordinate
Cryptography is the artwork of hiding messages, NOT writing on graves, which is a direct translation a pal of mine once asked. The major engine of encrypting a message makes use of a single key and a fast algorithm. The NIST normal is AES which might use key sizes of 128 bits, 192 bits, or 256 bits. Public-key cryptography is a cryptographic system that requires a secret key and a public key which are mathematically linked with one another. One key encrypts the plain textual content whereas the opposite decrypts the cipher text.
That’s essentially what happened to Sony when it mishandled its ECDSA (Elliptic Curve Digital Signature Algorithm) to sign software program on its PlayStation gaming system. Builders used static parameters quite than random keys, allowing hackers to solve the algorithm and decipher private keys. Side-channel attacks extract secret keys from chips or systems by monitoring and making sense of knowledge that’s “leaked” from a processor. These aspect channel assaults spy on things just like the chip’s energy consumption or temperature adjustments, the timing of processor occasions, and even the sound it makes.
As An Alternative, it plays a crucial function in establishing trust, exchanging keys securely, and verifying identities—functions that sit at the https://residenzpflicht.info/the-beginners-guide-to-what-you-need-to-know-to-get-started/ basis of safe communications. If somebody encrypts knowledge utilizing your public key, solely the corresponding private key can decrypt it. This makes uneven encryption ideal for secure communication between events who’ve never met or exchanged secrets earlier than. In the last 25 years, Elliptic Curve Cryptography (ECC) has become a mainstream primitive for cryptographic protocols and functions. ECC has been standardized to be used in key trade and digital signatures. This project focuses on environment friendly era of parameters and implementation of ECC and pairing-based crypto primitives, across architectures and platforms.
The smaller key dimension makes key era and signing much faster to use, decreasing any latency launched into the process. This can additionally be important for mobile devices or IoT units that have much less storage space and fewer computing power to resolve elliptic curve algorithms. ECC cryptography is rising in popularity relative to the Rivest-Shamir-Adelman (RSA) public-key encryption methodology used to safe knowledge in transit. While the RSA algorithm supplies encryption of email or information utilizing prime number factoring, ECC cryptography bases public keys on the looping lines on intersecting axis factors on a graph. We have been speaking about the way to bounce around a foolish elliptic curve in mild speed, but what about encryption?